Buy zxa.eu ?
We are moving the project
zxa.eu .
Are you interested in purchasing the domain
zxa.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy zxa.eu ?
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **

Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
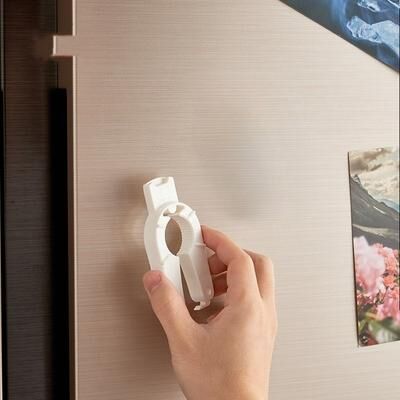
Multisell Products Hub Magnetic Bottle Opener For Household Mineral Water Plastic Beverage Bottles And Cap Opening, Kitchen Accessories Gadgets whiteEffortless Cap Opening for Everyday Kitchens Upgrade your routine with this 1 pcs Kitchen Accessories Gadgets Magnetic Bottle Opener for Household Mineral Water Plastic Beverage Bottles and Cap Opening designed for convenience and comfort. It makes...34,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Microsoft Office 5 DevicesMicrosoft Office 5 Devices. Lifetime licence for 5 devices, delivered digitally by email. Includes essential productivity applications for work and home, multilingual support where available, official download access and installation guidance. No physical product or shipping is required.249,95 £*Shipping: 0,00 £Secure redirect to the provider
-
Microsoft Office 3 DevicesMicrosoft Office 3 Devices. Lifetime licence for 3 devices, delivered digitally by email. Includes essential productivity applications for work and home, multilingual support where available, official download access and installation guidance. No physical product or shipping is required.169,90 £*Shipping: 0,00 £Secure redirect to the provider
-
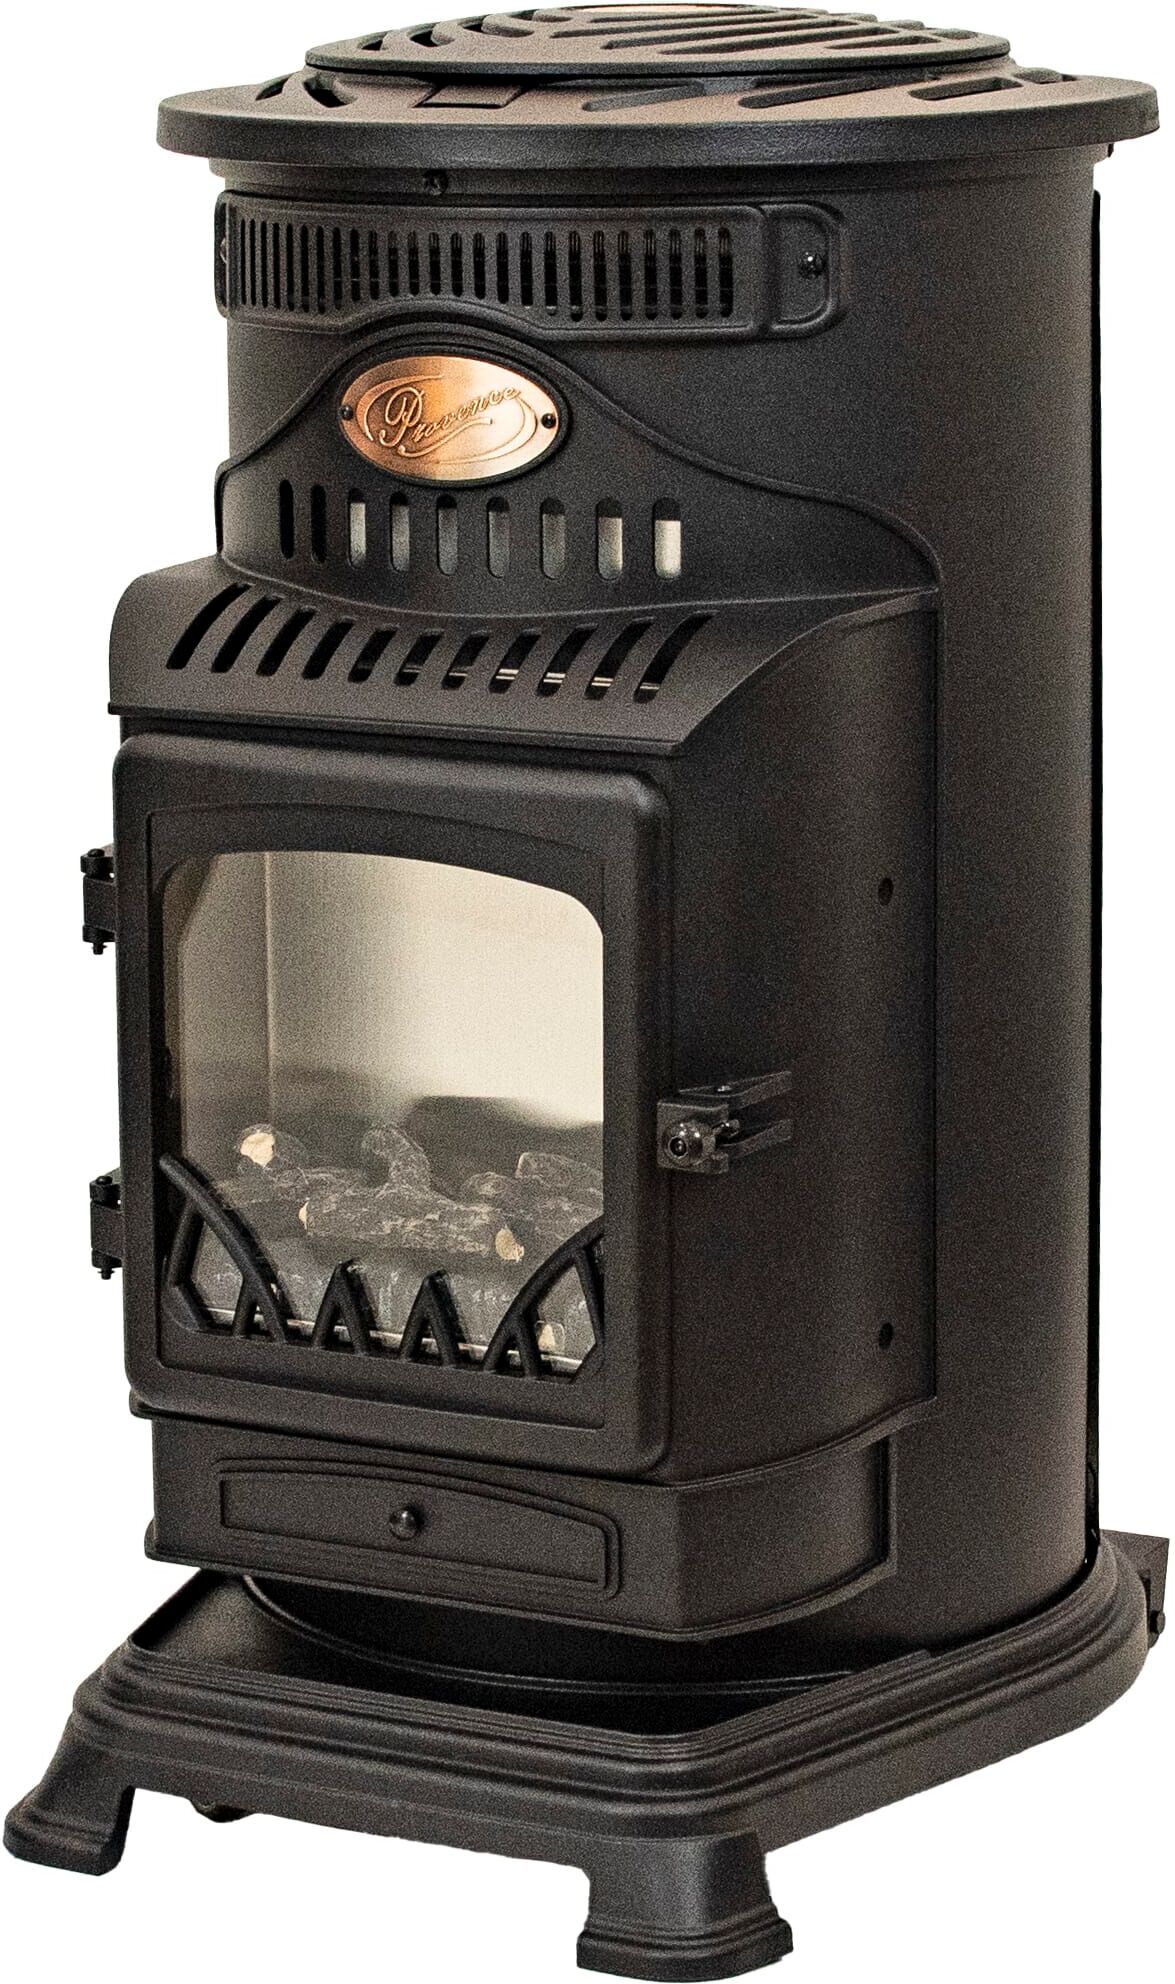
Universal Innovations Calor Gas 3kW Cream Provence Portable Gas HeaterCalor Gas 3kW Cream Provence Stove Portable Gas Heater – Country Chic Living Flame Heater The Calor Gas 3kW Provence Stove Portable Gas Heater – Cream is the perfect blend of traditional rustic charm and modern heating efficiency. Designed for character cottages, period properties and cosy interiors, this portable living flame stove gives instant, hassle free heat without the need for a flue, chimney or plug socket. With its cream finish and realistic flame effect, the Provence not only warms your home but also makes a stunning focal point, on or off. Built in wheels means you can take the warmth with you, from the kitchen to the conservatory. Key Features & Benefits Instant Living Flame Heat – Up to 3kW outp299,00 £*Shipping: 0,00 £Secure redirect to the provider

-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
Top-Angebote
Products related to Tpm:
-
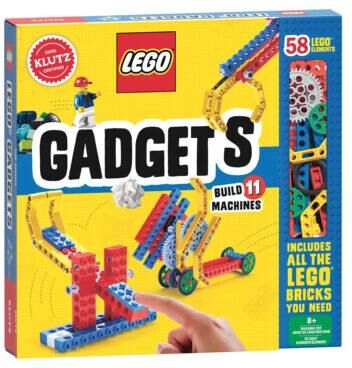
Klutz: LEGO GadgetsThis activity kit will have you building 11 machines including a gravity powered car and a wacky boxing robot. The fun doesn't stop once you've completed all of the projects in the book - open-ended prompts will inspire you to continue experimenting...24,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Universal Innovations Sahara Standard Patio Heater CoverKeep your patio heater protected from the elements all year round with a durable all-weather cover.The Sahara Patio Heater Cover is made from a heavyweight material and includes a waterproof inner lining, making it water and fire retardant. It has a full-length zip for easy fitting. Using thiscover will help to keep the gas nozzle and venturi free from dust and insects. This patio heater cover is the perfect companion for your 13kW Sahara Patio Heater and is suitable for most standard-sized patio heaters.43,56 £*Shipping: 5,00 £Secure redirect to the provider
-
Multisell Products Hub Magnetic Bottle Opener For Household Mineral Water Plastic Beverage Bottles And Cap Opening, Kitchen Accessories Gadgets whiteEffortless Cap Opening for Everyday Kitchens Upgrade your routine with this 1 pcs Kitchen Accessories Gadgets Magnetic Bottle Opener for Household Mineral Water Plastic Beverage Bottles and Cap Opening designed for convenience and comfort. It makes...34,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Microsoft Office 5 DevicesMicrosoft Office 5 Devices. Lifetime licence for 5 devices, delivered digitally by email. Includes essential productivity applications for work and home, multilingual support where available, official download access and installation guidance. No physical product or shipping is required.249,95 £*Shipping: 0,00 £Secure redirect to the provider
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
Similar search terms for Tpm
-
Microsoft Office 3 DevicesMicrosoft Office 3 Devices. Lifetime licence for 3 devices, delivered digitally by email. Includes essential productivity applications for work and home, multilingual support where available, official download access and installation guidance. No physical product or shipping is required.169,90 £*Shipping: 0,00 £Secure redirect to the provider
-
Universal Innovations Calor Gas 3kW Cream Provence Portable Gas HeaterCalor Gas 3kW Cream Provence Stove Portable Gas Heater – Country Chic Living Flame Heater The Calor Gas 3kW Provence Stove Portable Gas Heater – Cream is the perfect blend of traditional rustic charm and modern heating efficiency. Designed for character cottages, period properties and cosy interiors, this portable living flame stove gives instant, hassle free heat without the need for a flue, chimney or plug socket. With its cream finish and realistic flame effect, the Provence not only warms your home but also makes a stunning focal point, on or off. Built in wheels means you can take the warmth with you, from the kitchen to the conservatory. Key Features & Benefits Instant Living Flame Heat – Up to 3kW outp299,00 £*Shipping: 0,00 £Secure redirect to the provider
-
Universal Innovations Provence Hybrid 6kW Gas & Electric Portable Heater - BlackProvence Hybrid 6kW Flueless Gas & Electric Heater The Provence Hybrid 6kW combines a 4kW real gas flame fire with a built-in 2kW fan-assisted electric heater, giving flexible heating from a single cast iron unit. With no chimney, flue or mains gas connection required, it's designed to be genuinely portable, running from a butane cylinder for the gas element while offering electric heating as a fan-assisted alternative or supplement. Traditional cast iron construction gives good heat retention and a realistic flame effect, while castor wheels make it easy to reposition between rooms. Variable heat control allows output to be adjusted to suit the space, and built-in safety features — an Oxygen Depletion Sensor (ODS) and flame failure cut-off — are standard for indoor gas heater use. Key Features & Benefits349,00 £*Shipping: 0,00 £Secure redirect to the provider
-
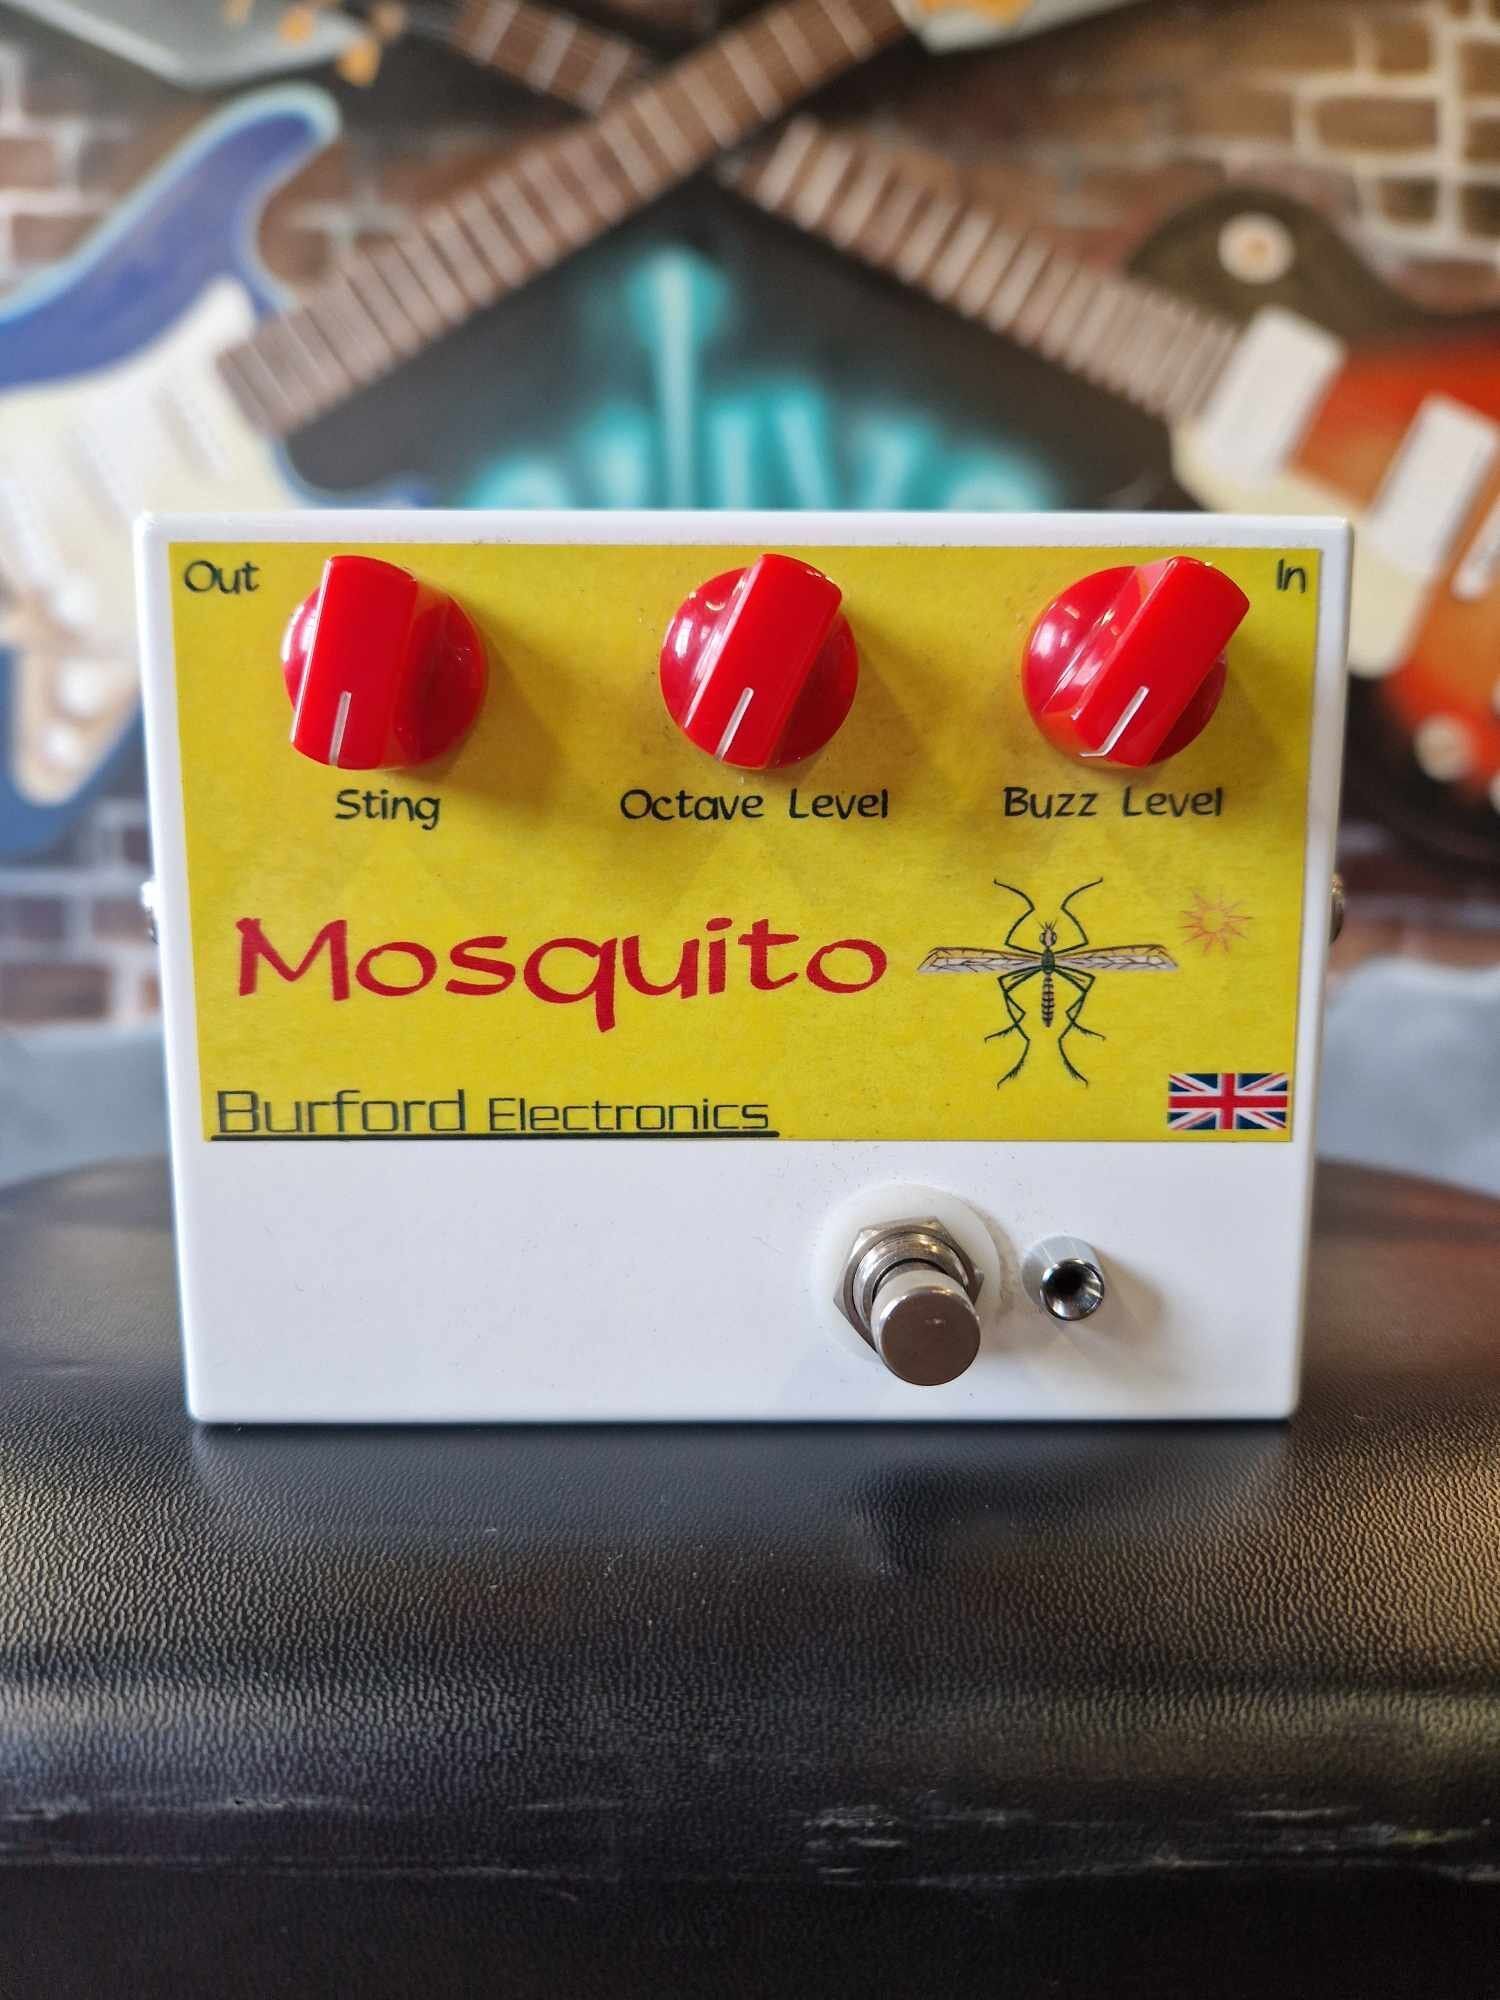
Burford Electronics Mosquito Fuzz Pedal Original - RefurbishedThis is a Burford Electronics Mosquito Fuzz Pedal. The Mosquito is a Fuzz/Octave pedal with a pretty unique sound, being closer to a fuzz more than a distortion this pedal delivers high octane fuzz sounds that will leave a sting. Here's what Burford Electronics say about the Mosquito Pedal: “A unique Octave up fuzz, which will give you pure fuzz on one twist of a knob & octave fuzz on one twist of another knob. So you can have your fuzz setting for a rich body & add octave fuzz to it or turn the fuzz down & just use the octave fuzz control for cutting lead. There is also a control called Sting, this is a tone filter that alters the voice of the octave from sharp to mellow. The octave is not over the top, on the lower register it is quite subtle, you can even play power chords and it holds together extremely well. Without that horrible modulation that is associated with some analogue octave up pedals, even some of the legendary expensive ones. Try soloing somewhere from the 8th fret upwards, it is very responsive and particularly so around 12th/15th fret and even higher. Neck and back pick ups give different sounds. Even playing positions will give different responses.”120,00 £*Shipping: 0,00 £Secure redirect to the provider
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.